Next.js information leak via "use cache" (CVE-2026-119790)
In this article
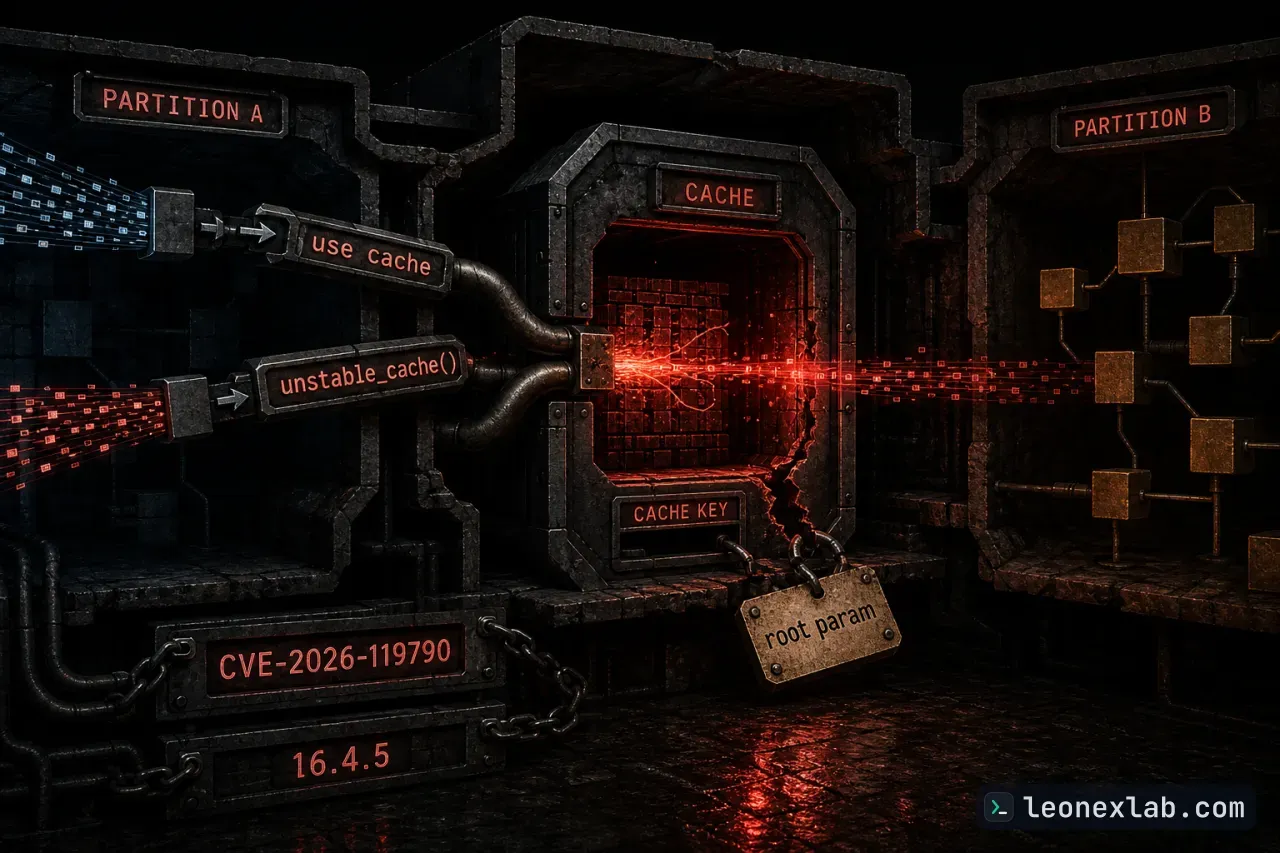
A Moderate-severity vulnerability in Next.js allows cached data for one root param value to be returned to requests belonging to a different root param value. The bug appears when the same 'use cache' function is called both directly during render and through unstable_cache(), and that function reads a root param. The cause is a race condition that occurs when a new process starts up. Version 16.4.5 is the patched release.
Scope of impact
The vulnerability was published in the vercel/next.js repository, affecting the next package on npm. The affected versions range from 16.3.0 to 16.4.4, and the fix is 16.4.5. The vulnerability carries the CVE ID CVE-2026-119790 and the GHSA ID GHSA-mfr8-8qww-v76h. Its severity is rated Moderate.
Root params are the route parameters of the root layout. Applications commonly use them to partition data, for example by locale. So when the data of one value leaks into another, it is an information leak across scopes that the application is meant to keep separate.
Failure mechanism
When the process undergoes a cold start (cold process start), the cross-request deduplication mechanism falls into a race. A call to unstable_cache() can join the in-progress cache fill of a concurrent direct call and receive that call's result as its own. This lets it bypass the root param check that would otherwise reject this case.
Afterwards, unstable_cache() stores the result it just received under a cache key that does not contain the root param. As a result, subsequent requests with a different root param value receive this same cache entry, until the entry is revalidated or evicted. In other words, data generated for one root param value is returned to requests for other values.
Exploitation conditions and workarounds
Exploitation requires the request calling unstable_cache() to arrive at exactly the moment when the function's first fill after process startup is still in progress. Outside this race window, such nesting already throws an error on its own: using 'use cache' inside unstable_cache() is not supported.
Avoiding nesting 'use cache' inside unstable_cache() is cited as a complete workaround.
Upgrade to the patched version 16.4.5 to fix the bug at its root.
CVSS assessment and weakness type
Attack Vector is Network, meaning it can be exploited remotely over the network.
Attack Complexity is Low and Attack Requirements is Present: certain deployment and execution conditions must exist for the attack to succeed.
Privileges Required is None and User interaction is None: the attacker needs no privileges and no participation from other users.
Impact on the vulnerable system: Confidentiality is Low, while Integrity and Availability are None.
Impact on subsequent systems: Confidentiality, Integrity and Availability are all None.